Features
access and security
Staff see and do what their role allows, at the branches they work in. Sensitive actions need a second person, and everything that changes is written down.
who can do what
- Owner, administrator, manager, agent, maintenance and read-only roles
- Staff limited to their own branches
- Permissions enforced on the server, not just hidden buttons
- Invitations by link; deactivation signs the person out at once
sign-in
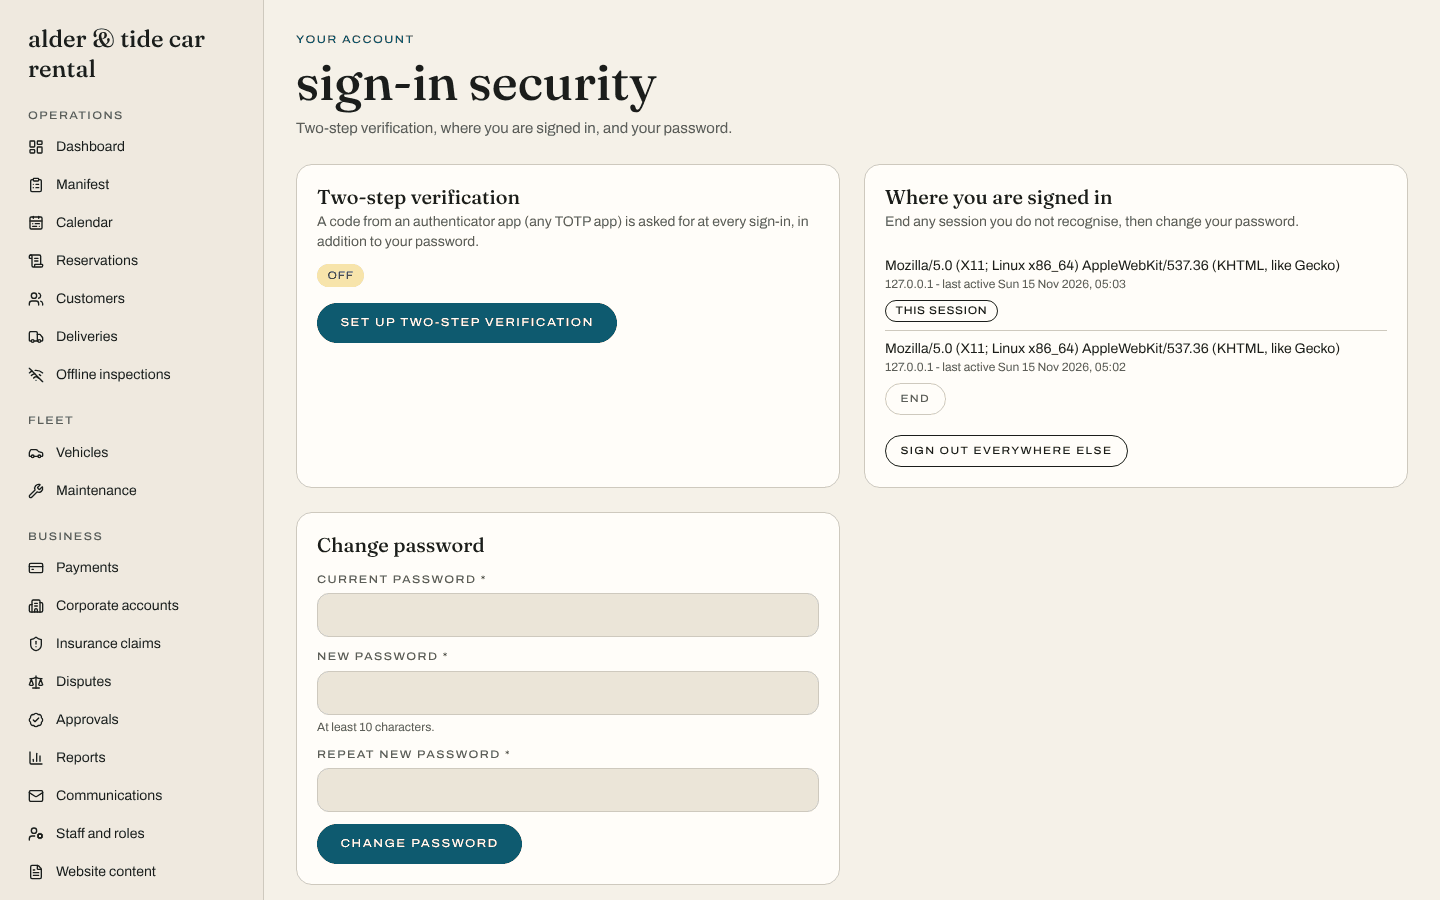
- Two-step verification with any authenticator app, with recovery codes
- Optionally required for all staff
- Each code works once; repeated wrong codes lock the step
- Session list with remote sign-out, and password reset by emailed link
checks and records
- Second-person approval for large refunds and for security settings
- Nobody can approve their own request
- Audit log of who changed what and when
- Card details never touch the software
see if it fits your fleet
Tell us about your business. We reply by email, usually with a few questions and an offer to walk you through the product.